White Paper
08/30/2026
Campus Consortium Foundation
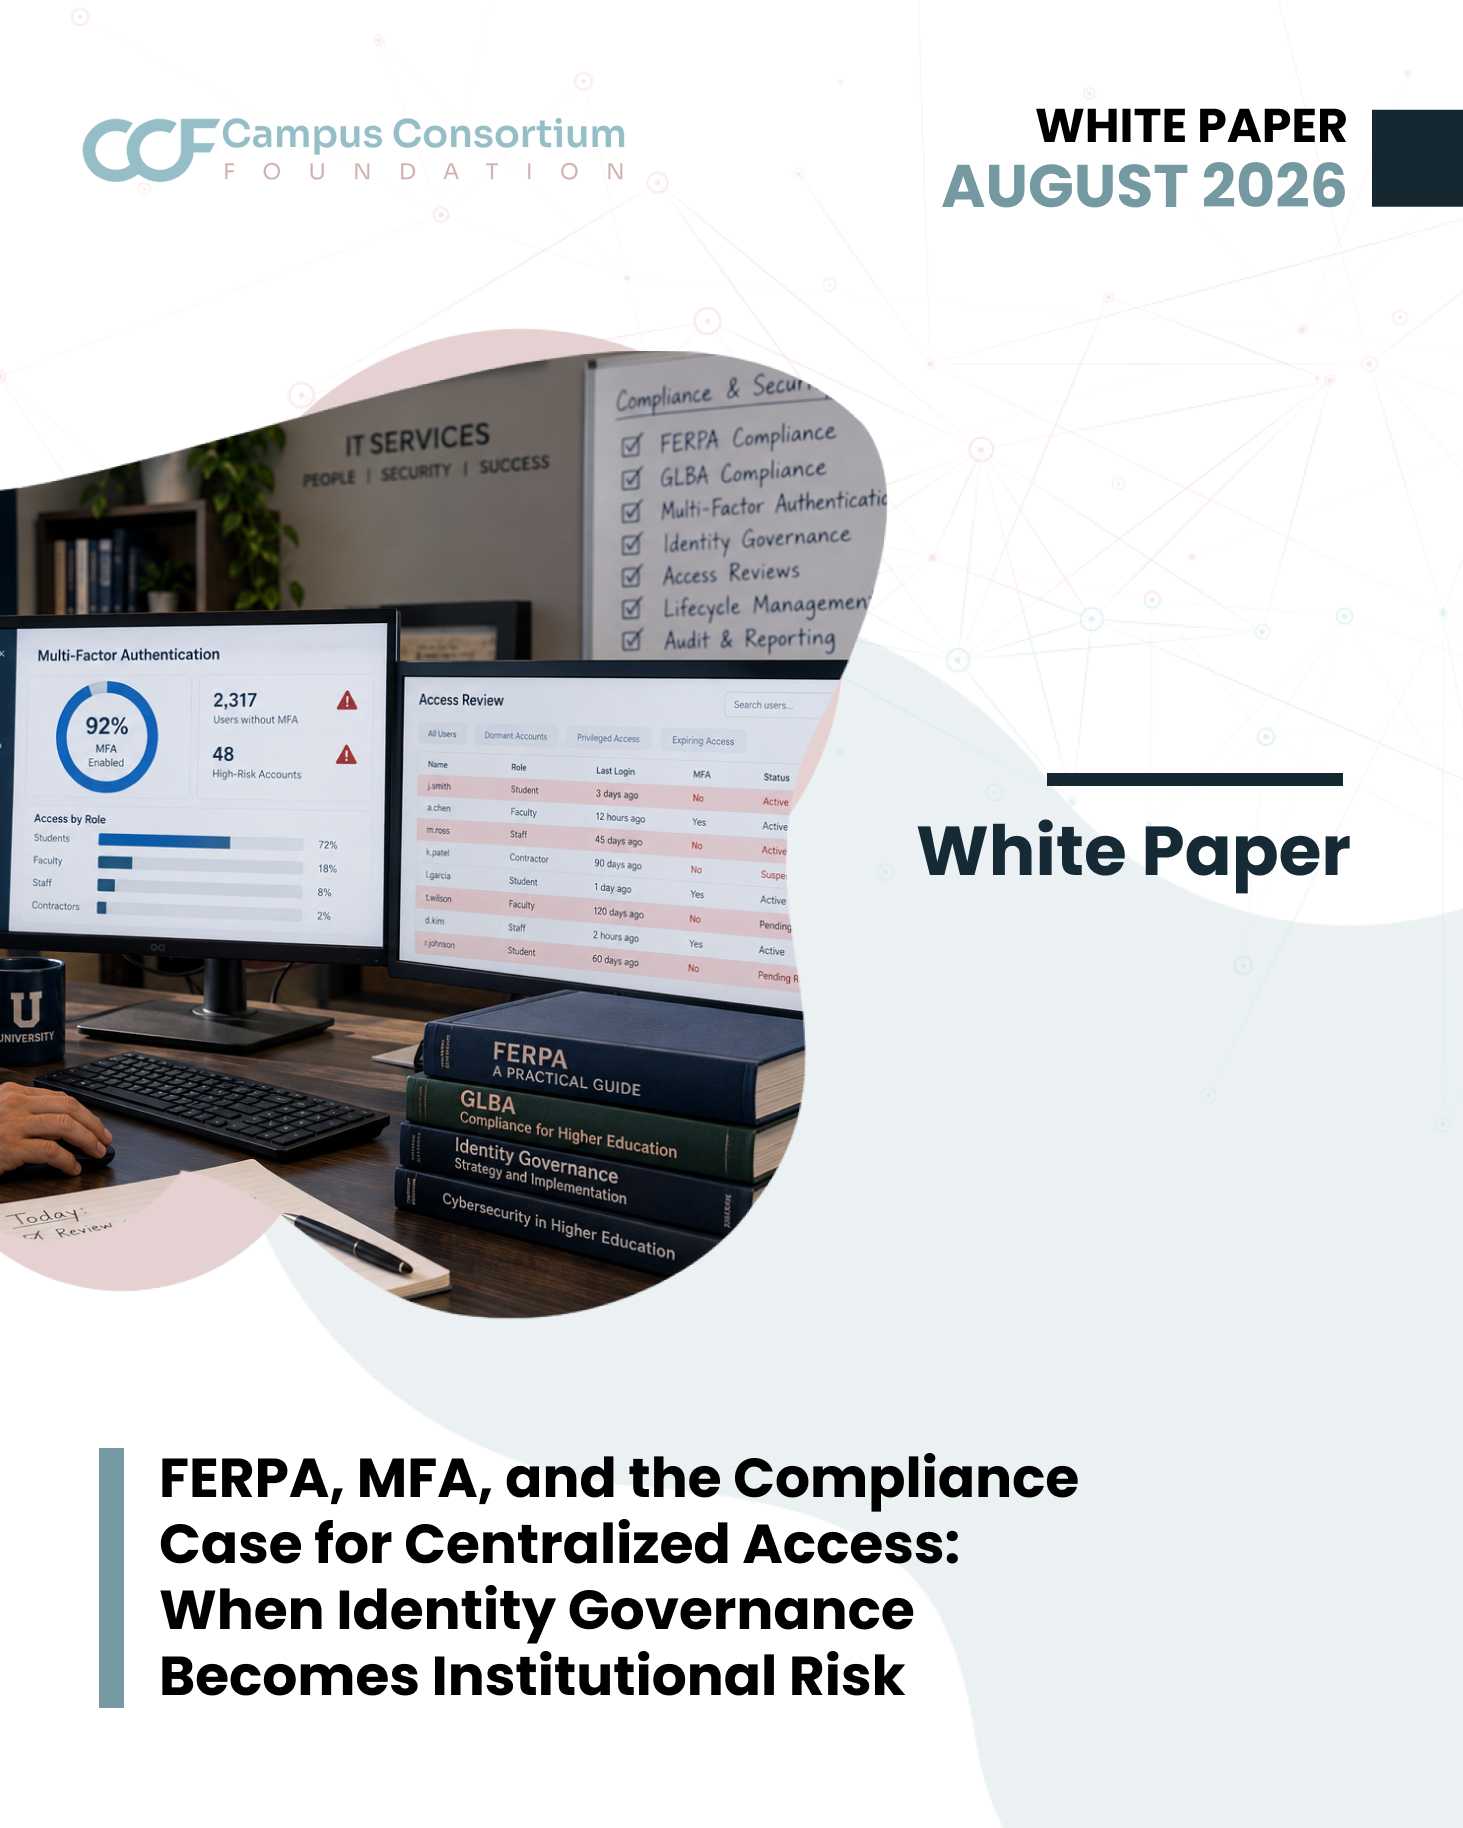
FERPA, MFA, and the Compliance Case for Centralized Access: When Identity Governance Becomes Institutional Risk
Why Read This Research
MFA alone cannot address the identity and access risks facing higher education. This research examines how FERPA and GLBA compliance challenges emerge across campus roles and how centralized identity governance, automated access controls, and stronger lifecycle management can reduce security, compliance, and operational risk.
Key Questions Answered
- Why is MFA alone not enough?
- Where do FERPA and GLBA access risks occur across campus?
- Why are Registrar and Financial Aid systems particularly sensitive?
- Why do adjunct faculty create deprovisioning risks?
- How do graduate assistants create dual-role identity challenges?
- What happens when compliance requirements are not met?
- How does fragmented access management increase institutional risk?
- How can centralized identity governance strengthen compliance?
- What does role-specific access management look like?
- How can institutions move toward continuous compliance monitoring?
Features
- Research Focus: FERPA, MFA, GLBA, Identity Governance, Access Management, Compliance
- Future Campus Impacts: Cybersecurity, Data Protection, Regulatory Compliance, Audit Readiness, IT Efficiency
- Audience: CIOs, CISOs, Compliance Officers, IT Directors, Identity Architects, Higher Education Risk Leaders
- Research Approach: CCF Higher Education Identity Lifecycle Practitioner Survey, institutional role analysis, and secondary research
- Authors: Campus Consortium Foundation Research Team
- Research Availability: August 2026
Table of Contents
- The Compliance Landscape in Higher Education
- Compliance Through the Lens of Campus Roles
- Why MFA Alone Is Not Enough: The Governance Gap
- What Happens When Compliance Fails: The Institutional Consequence Analysis
- The Problem With Fragmented Access Management
- Centralized Identity Governance as the Compliance Foundation
- Institutional Case Study: Closing the Adjunct and GA Compliance Gap
- Risk Reduction Through Centralized Identity Controls
- Emerging Compliance Strategies
- Compliance-Focused Identity Platforms: Evaluation Framework
- Future Outlook
- Strategic Recommendations for CIOs, CISOs, and Compliance Officers
- Conclusion